Cloudflare and BunnyCDN origin lock

Origin lock accepts HTTP/HTTPS only from official CDN ranges. Direct hits to the server IP on 80/443 are dropped.

  1. Confirm orange-cloud DNS already works.
  2. DDoS / CDN → Refresh CF IPs (lsf --cf-refresh).
  3. Set CF_ORIGIN_ONLY=1 in lsf.conf.
  4. Enable / Restart.

Same pattern for Bunny: Refresh Bunny IPs and BUNNY_ORIGIN_ONLY=1. Refresh often — Bunny edges rotate. If a refresh leaves the list empty, LSF skips origin-lock instead of dropping all HTTP.
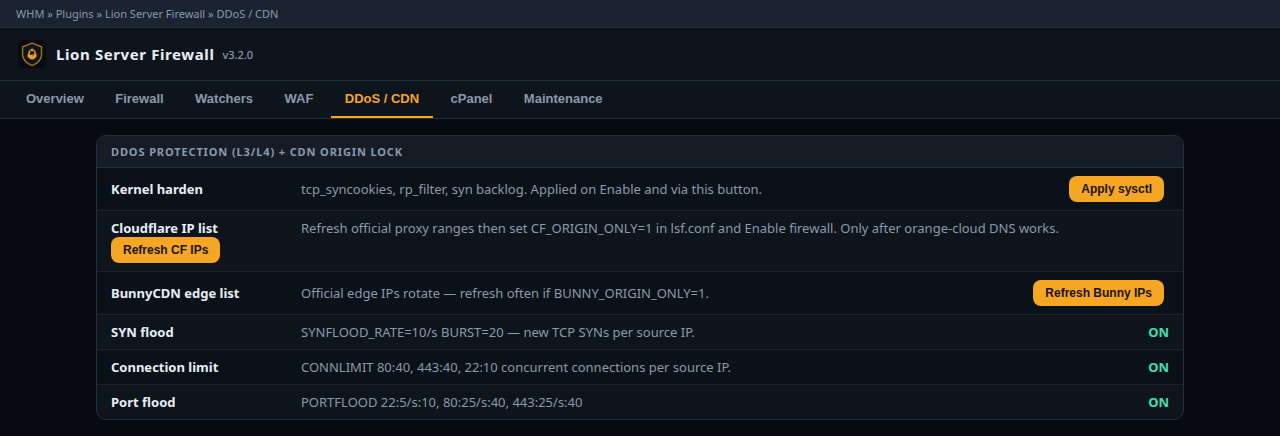
DDoS / CDN tab

  • lsf, ddos
  • 0 Users Found This Useful
Was this answer helpful?

Related Articles

GeoIP country blocking in LSF

CC_DENY="CN,RU,KP" CC_ALLOW="GR,CY,DE" CC_DENY drops all inbound from those countries. CC_ALLOW...

LSF WAF false positive

LSF does not replace WHM → ModSecurity Vendors (OWASP CRS / Atomicorp). It loads a supplementary...

LFD and PSAD — brute force and port scans

LFD watches SSH, FTP, mail, Exim, cPanel and ModSecurity failures. Default: 5 hits in 300 seconds...

Which ports does Lion Server Firewall open

Default TCP_IN: 20, 21, 22, 25, 26, 53, 80, 110, 143, 443, 465, 587, 993, 995, 2082, 2083, 2086,...

Locked out of the server by LSF

TESTING mode: wait up to 5 minutes for the auto-flush. Lionhost KVM / VNC / IPMI as root: lsf...